Is Cybersecurity Affected by Artificial Intelligence?
How AI is transforming cyber defence, empowering attackers, introducing new vulnerabilities, and reshaping the future of digital security.
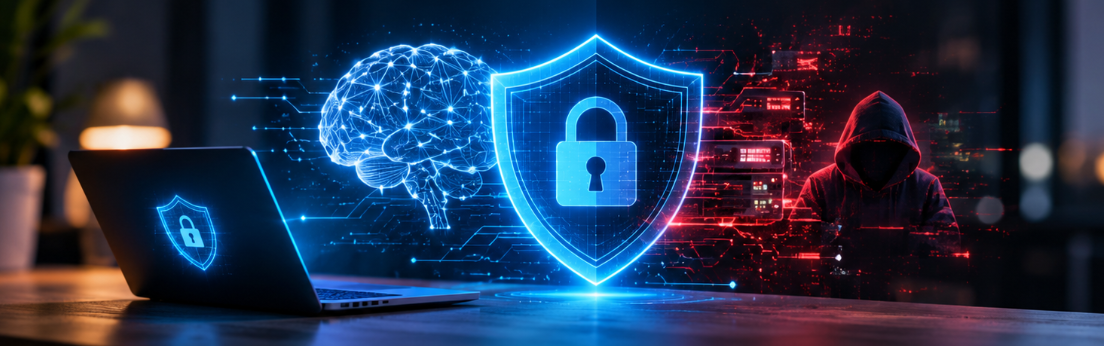
Artificial Intelligence is changing pretty much every part of technology and cybersecurity. It can improve security by helping teams detect any suspicious activity, however, threat actors can use this to create very realistic phishing attacks.
Yes and no.
Artificial Intelligence has become a key part of security. It can analyse large amounts of data quickly to find anomalies and automate mundane tasks. However cyber criminals can also use this to develop more realistic social engineering attacks, automate and create new vulnerabilities.
This post will look at how AI affects cybersecurity along with the benefits, issues, examples of how it can be used, new risks and what the future looks like.
1. What is Artificial Intelligence?
An Artificial Intelligence is any computer system which can perform tasks typically completed by humans. These tasks can include learning, pattern recognition, prediction and understanding natural language.
Many AI techniques can be used in cybersecurity. These include Machine Learning, deep learning and Natural Language Processing. These can detect any anomalies.
Traditional cybersecurity relies on rules, known threats and alerts. With the fast moving nature of attacks, it can be difficult to keep up. AI can compliment traditional tools to improve by learning from data. This can detect:
- Abnormal logins and misuse of credentials.
- Malicious features of emails.
- Unusual traffic.
AI should be seen as a multiplier to help security teams.
2. Benefits of AI
A great benefit of AI is that it can process lots of data quickly.
A. Threat Detection
Organisations will have a large amount of telemetry coming from many sources such as network, authentication, application and endpoint logs. This would be extremely hard to manually analyse. Machine Learning can create a baseline of what is considered normal and detect any anomalies:
- Multiple failed logins or impossible logins.
- Unauthorized access to sensitive files.
- Unusual outbound traffic.
- Activity outside of working hours.
B. Incident Response
When responding to a breach, time is of the essence. AI supported platforms can help the security operations centre to prioritise alerts, correlate related events and respond with pre-defined actions. For example, isolating an infected endpoint or locking an account. This reduces alert fatigue and means analysts can focus on complex investigations. Any high impact automated actions should have strict permissions.
C. Phishing and Email Protection
Phishing is one of the most common ways of starting an attack. Instead of using basic filtering, AI models can check the content of the email, sender, past interactions and any links or attachments to detect any sophisticated impersonation.
D. Malware and Behavioural
Traditional anti-virus can only protect against malware by using known signatures. This can leave systems open to zero day attacks. AI supported Endpoint Detection and response tools can detect unusual behaviour such as:
- Unusual processes.
- Unauthorized changes to files.
- Memory injection.
However, this AI detection can sometimes cause false positives and false negatives.
E. Vulnerability Management
Enterprises have thousands of applications, libraries and infrastructure. AI tools can help by correlating the vulnerability data. This can summarise technical advisories, show what is exposed on critical assets and prioritise remediation.
3. Issues
Whilst AI can improve security it can also make attacks easier and increase the attack surface.
A. Realistic Phishing
Threat actors can use generative AI to create extremely realistic phishing emails in multiple languages. You can no longer rely on bad grammar as a red flag.
B. Deepfakes
AI tools can create realistic audio, images and videos. Threat actors can use deepfakes to impersonate members of staff, executives or vendors. For example, cloned voices can be used to pressure employees into authorising fraudulent wire transfers or provide credentials. Strong out of band verification is now essential.
C. Automated Cyber Crime
Threat actors can use AI to automate reconnaissance, scanning for vulnerabilities, creating payloads and managing campaigns. Whilst this won’t make a novice an elite hacker, it can allow them to perform attacks at a faster rate and scale. However, they will still need access to infrastructure, and human error.
D. Social Engineering
AI can scrape data from the internet and social media to personalise pretexting scenarios depending on what role the target has, what industry they’re in and how they communicate. This makes them much harder to manipulate.
E. New Attacks
Using Large language models and AI agents can bring new risks. Traditional application security may not cover these. OWASP top 10 for Large Language Model Applications shows some key risks:
- Prompt injection – Manipulate an Large Language Model by providing prompts.
- Sensitive information exposure – Exposing sensitive information from training data.
- Data poisoning – Poisoning the training or reference data.
- Model theft – Stealing the models.
- Overstepping – Giving too much permission to AI agents.
4. Examples
AI is used in almost every part of enterprise security:
- Network Security – Detect unusual traffic, lateral movement and command and control.
- Email Security – Detect social engineering, Business Email Compromise and malicious content.
- Endpoint Security – Detect unusual process behaviour to block ransomware and fileless malware.
- Fraud Detection – Detect unusual financial transactions.
- Security – Correlate alerts, enrich threat intelligence and speed up incidents.
- Identity – Detect unusual authentication requests.
- Vulnerability Management – Prioritise patching by correlating vulnerabilities with critical assets.
- Cloud Security – Detect mis-configuration, API abuse and unusual activity.
5. AI vs Traditional Cybersecurity
Does AI replace traditional cybersecurity? No, it works best when used together.
- Rules – Traditional uses rules, whilst AI learns from data.
- Signatures – Traditional uses known signatures, whilst AI detects new anomalies.
- Alerts – Traditional can have manual alert triage, whilst AI can automate.
- Threshold – Traditional uses set thresholds, whilst AI adapts.
Basic security controls such as firewalls, encryption, least privileged access, multi-factor authentication, secure configurations and regular patching cannot be ignored. AI can compliment these.
6. Challenges
Using AI tools can pose challenges:
- False positives/negatives – Over-sensitive models can cause too many alerts. Poorly configured models may miss real attacks.
- Data privacy – AI models need large amounts of data, if you don’t classify and sanitise your data you may expose sensitive information.
- Not Transparent – Many deep learning models cannot explain why an event was flagged. Security needs to be able to see why alerts are being raised to perform proper audits.
- Over reliance – Blindly trusting AI can cause errors and missing context. Human oversight is required.
- Cost – Building, configuring and maintaining AI security pipelines requires specialist skills, good data, computing and validation.
7. Best Practice
To get the most out of AI without any unnecessary risks, follow best practice guidelines from NIST, CISA and OWASP:
- Limit your access – Limit what data and permissions your AI applications and agents have.
- Protect your data – Classify, encrypt and sanitise your data before using it in AI models or third party AI.
- Human Oversight – Don’t blindly trust AI recommendations. High impact actions should have human approval.
- Monitor your AI – Monitor your AI to ensure no abuse. Check for model drift, API usage and access.
- Test your AI – Test your Large Language Model applications using adversarial testing and red teaming to find prompt injection and data leakage flaws.
- Keep patched – Ensure all your AI frameworks, dependencies, models and infrastructure are regularly patched.
- Staff Training – Update your security awareness to help staff identify AI generated phishing, voice cloning and social engineering using deepfake.
8. Future of Cybersecurity
As AI becomes more advanced cybersecurity will change:
- AI will help correlate telemetry from different tools, automate tier one investigations and suggest remediation.
- AI Security Posture Management – Securing models, training, vector databases and agents will become a key part of enterprise security.
- AI will help with large amounts of data and mundane tasks. This allows human to focus on threat hunting, risk management and complex decisions.
- Zero-trust verification – With the rise of synthetic media, organisations will rely on cryptography, phishing-proof multi-factor authentication and strict out of band approvals.
- Formal AI – More regulations and formal requirements will be put in place.
9. Conclusion
Yes cybersecurity is affected by AI.
The use of AI is changing both sides of cybersecurity. It can help security teams detect threats quicker, automate responses and manage complex environments, but can also help threat actors scale social engineering attacks, automate and attack AI driven applications.
AI isn’t a magic bullet and should never be seen as replacing good security engineering. The future of cybersecurity will be for those who can use AI to compliment good security practices with strict governance, monitoring and skilled people.
References
- ENISA Threat Landscape 2026 – European Union Agency for Cybersecurity
- Microsoft Digital Defense Report 2025 – Microsoft
- OWASP Top 10 for Large Language Model Applications – OWASP Foundation
- Cybersecurity, Privacy, and Artificial Intelligence – National Institute of Standards and Technology
- AI Risk Management Framework: Generative AI – National Institute of Standards and Technology
- Careful Adoption of Agentic Artificial Intelligence Services – Cybersecurity and Infrastructure Security Agency & International Cybersecurity Partners
Disclaimer: This article is for educational purposes only. It shows guidance and research available publicly about cybersecurity.
About the author
- Full-stack developer and cybersecurity student focusing on secure web apps, Linux configurations, and automation.
Comments
Join the discussionNo comments yet. Be the first to comment.